Related Topics:
Argentina Network Security Research-
Norwegian Cost Network Security Equipment QSFP28
QSFP28 (Quad Small Form-Factor Pluggable 28) enables 100G transmission by aggregating four parallel 25G electrical lanes, delivering an optimal balance of bandwidth efficiency, power consumption, and deployment flexibility. At the center of this transition is QSFP28, a compact, high-performance optical transceiver form factor designed specifically for 100-gigabit data rates. PacketFalcon provides permanent 24 x 7 access to 1G, 10G, 25G, 40G and 100G networks for detailed analysis, including. Let's take a look at different factors that could affect 100G QSFP28 optical module cost. While optical transceiver development has gotten simpler over the years, it does involve full engineering development to design, validate, and qualify. Affordably priced, with full support for Layer 2, Layer 3, IPv4 and IPv6 networking protocols at no additional cost for. Huawei High Speed Transceiver,QSFP28,1310nm,100G,-2. By providing four lanes of 25G, QSFP28 enables a streamlined upgrade path from lower-speed.
[PDF Version]
-
Is debugging network security equipment difficult
Disassembly and debugging are crucial skills for network security and forensics professionals. These techniques allow analysts to examine code at a low level, uncovering vulnerabilities, reverse engineering software, and analyzing malicious programs. This guide is designed to provide professionals with a structured approach to debugging for security, equipping them with. This comprehensive guide will show you how to combine packet sniffers with firewall logs to create a powerful network security debugging system that can detect, diagnose, and respond to threats in real-time. Note: This is a simplified illustration. Real-world implementations involve more complex. Debugging these systems can be challenging due to their complexity and the need for coordination between different parts. This comprehensive guide provides professionals and students with practical strategies to effectively diagnose, troubleshoot, and optimize their.
[PDF Version]
-
What are the three categories of network security devices
Network security includes three essential components: Hardware network security. This includes physical devices that protect and monitor computer networks, such as firewalls, routers, and network security appliances (NSAs). In this article, we will explore common types of network security devices, appliances and technologies that form a robust, multi-layered security strategy, including firewalls, intrusion prevention systems, and endpoint protection solutions. While networking security tools have traditionally been implemented as on-prem network security hardware or virtual. Network security devices are essential tools that help prevent unauthorized access, data breaches, and cyberattacks. Whether you're a business owner or an IT professional, understanding the.
[PDF Version]
-
Burkina Faso CIF price network security equipment SFP
Buy networking equipments online in Burkina Faso. Fast shipping, competitive prices, and expert support for businesses and resellers. The Cisco Meraki MX are multifunctional security and SD-WAN enterprise appliances with a wide set of capabilities to address multiple use cases–from an all-in-one device. Organizations of all sizes and across all industries rely on the MX to deliver secure connectivity to hub locations or. We supply Cisco, Juniper, Mikrotik, Huawei & Ubiquiti networking equipment across Burkina Faso. Businesses across Burkina. The network security firewall market in Burkina Faso focuses on devices and technologies that protect networks from unauthorized access and cyber threats. Network firewalls are essential for maintaining network security and integrity. It is based on the information available at the time it was completed on May 31, 2024. Overview of the Model and. GPON Class C+ SFP OLT module, 1490 (Tx)/1310 (Rx), Industrial Temp Cisco SFP-GPON-C-I are in high demand.
[PDF Version]
-
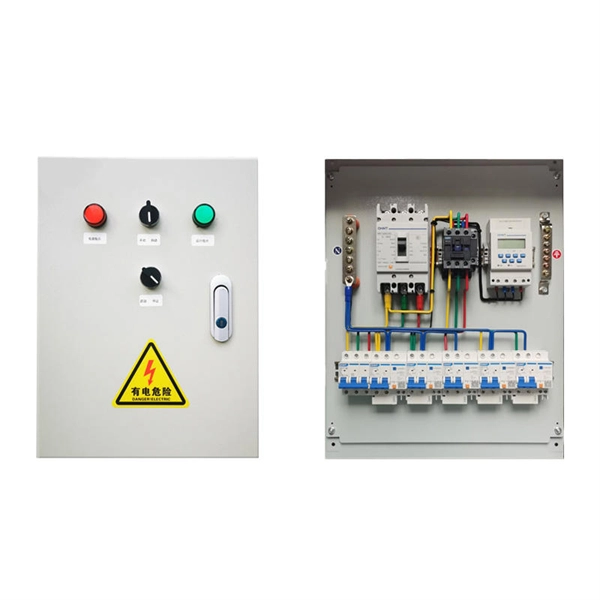
Argentina Network Cabinet
Prior to, the administration of the was organized under the Royal Ordinance of Administrators (Spanish: Real Ordenanza de Intendentes) issued on 28 January 1782, under which there were eight intendencias, each with a governor reporting to the viceroy. The governor had the police, finance, and the military under his direct control, and his lieutenant administered the courts. At first the revolutionaries retained the same system, only gradually dispersin.
[PDF Version]
-
SFP of RoHS Network Security Equipment in Five Central Asian Countries
Below, we will examine the EU RoHS Directive in relation to key equivalent regulations in major export markets for electronic equipment, including SASO RoHS in Saudi Arabia, China RoHS, EAEU RoHS, UK RoHS, and other relevant regulations. Restriction of Hazardous Substances (RoHS) is a comprehensive piece of legislation specifically applicable to EEE, which usually requires the restriction of certain categories of hazardous substances concentration in EEE and/or the labeling of them. Regulations in some markets cover both. RoHS stands for Restriction of Hazardous Substances. With over ten years expertise in global RoHS legislative and product safety conformity assessment requirements, Joyce also works closely with customers to assist them in.
[PDF Version]
-
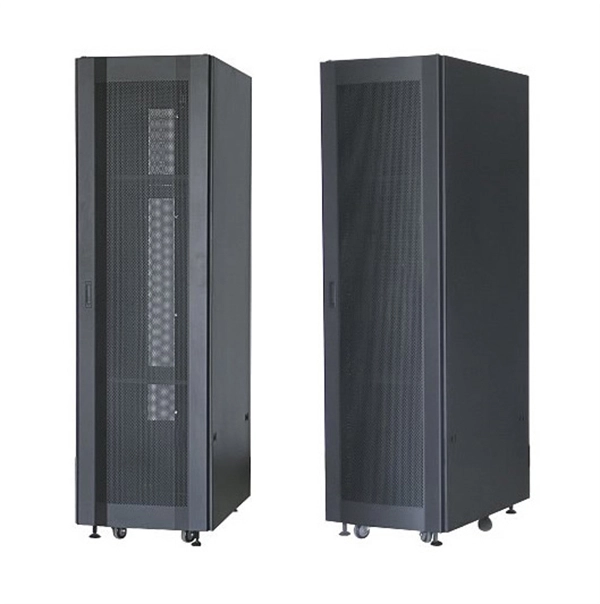
Network rack data center placement
The placement of racks should allow for easy access to equipment and proper airflow. Racks should be aligned in hot aisle/cold aisle configurations, where the fronts of the racks face each other (cold aisle) and the backs of the racks face each other (hot aisle). It provides a clear overview of the physical layout of the rack, including the placement and positioning of servers, switches, storage devices, and other. In this article we talk about proper placement of equipment in a rack, in other words, we take a systematic look at the operation of a server rack: from drawing up a plan and installation to wiring labeling. In high-density environments, planning the server rack layout in advance is crucial.
[PDF Version]